
Let users log in with Okta
Create an OIDC web app integration in Okta, add Tadabase's callback URL, and paste the Base URL, Client Id and Client Secret into your app.
- Verified Nov 17, 2026
- Classic builder
On this page
Okta is an identity provider that many companies use to manage their staff's sign-ins. Connect it to your app so the people you assign in Okta can log in with their Okta account.
1. Turn on Okta and copy the callback URL #
- Open User Settings In the builder, open Settings > User Settings, General tab.
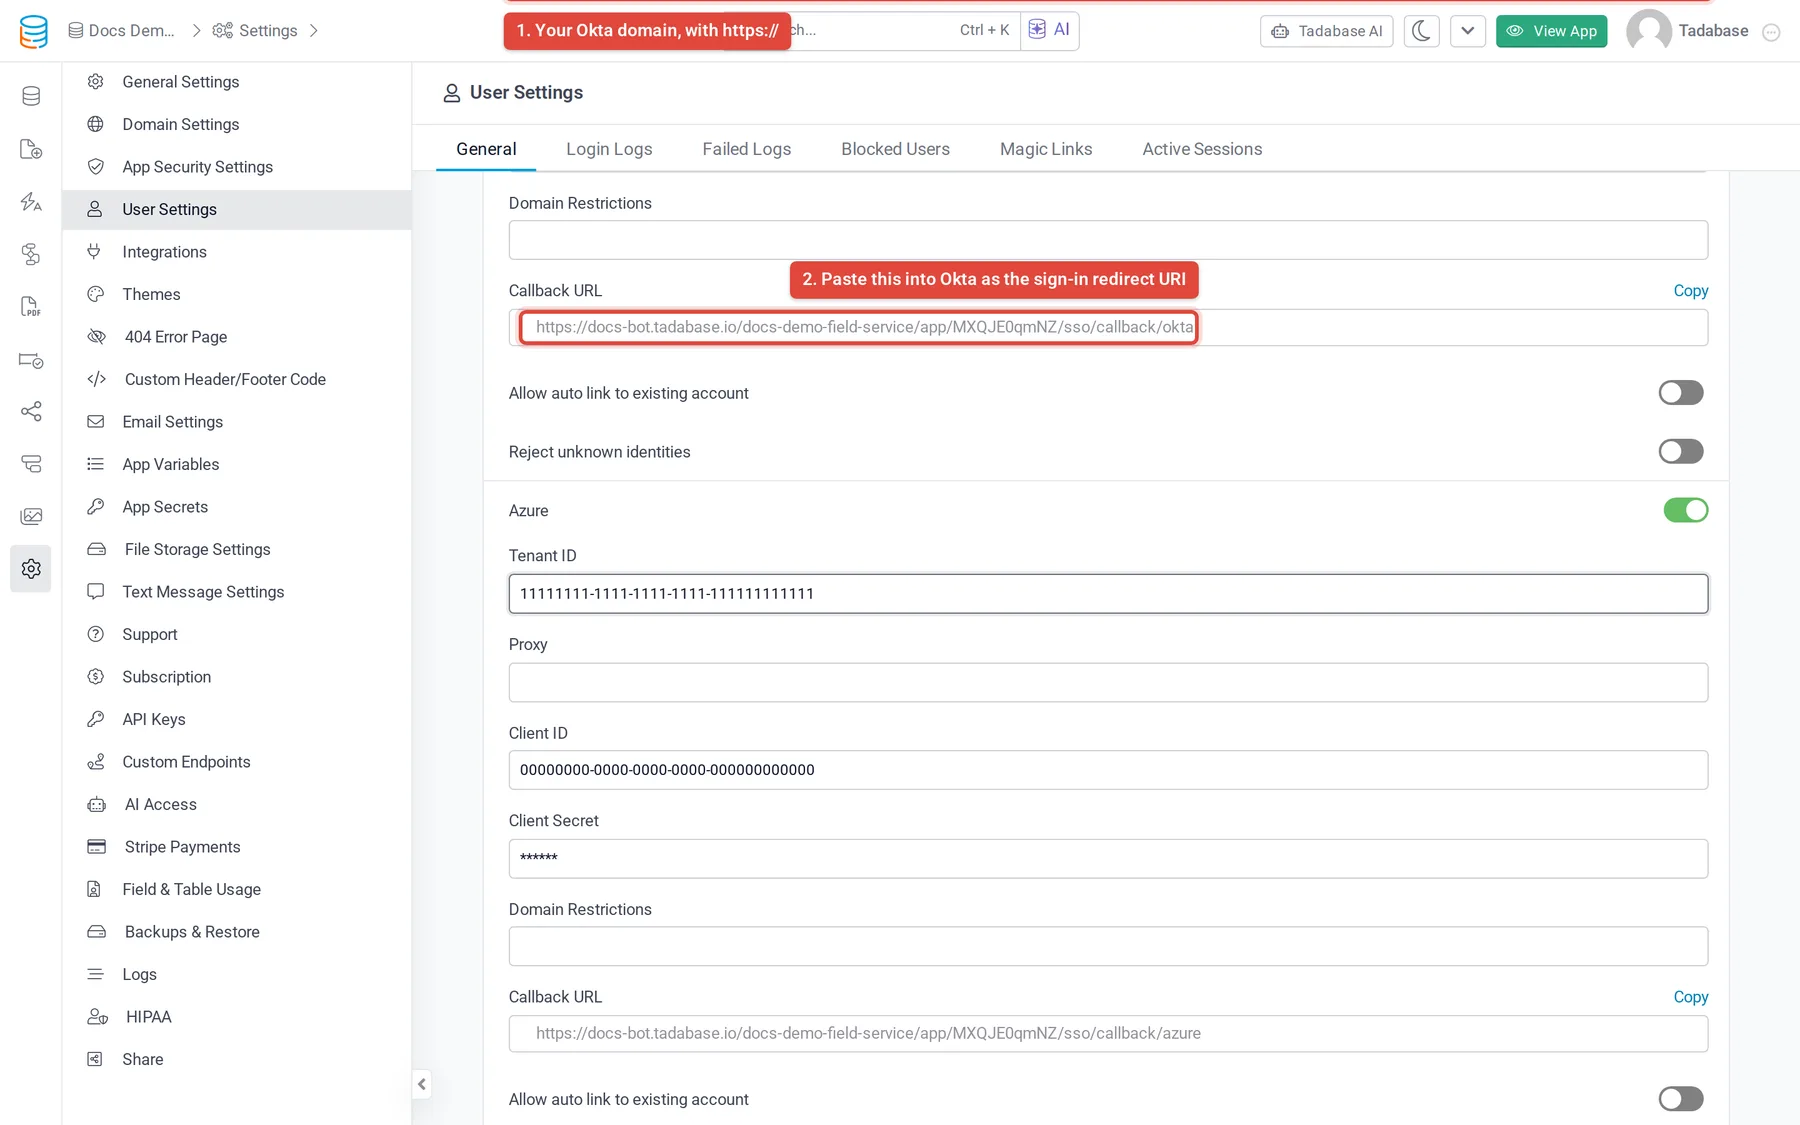
- Turn on Okta Under Login/Signup Methods, click the Okta icon. The Okta card opens.
- Copy the callback URL Click Copy next to Callback URL.
2. Create the app integration in Okta #
- Create a new app integration In the Okta admin console, open Applications and create a new app integration. Choose OIDC - OpenID Connect as the sign-in method and Web Application as the application type.
- Name it Give the integration a name (and a logo if you like) so your users recognise it.
- Set the sign-in redirect URI Paste the Callback URL from Tadabase as the sign-in redirect URI.
- Assign people Choose which Okta users or groups may use the integration. This controls who can sign in through Okta; it does not create users in your Tadabase app.
- Copy the keys Save the integration and copy its client ID and client secret.
3. Fill in the Okta card #
| Field | What to enter |
|---|---|
| Base URL | Your Okta domain with https:// and nothing after it, for example https://your-company.okta.com. Tadabase adds /oauth2/, /oauth2/ and /oauth2/ to it. |
| Client Id | The integration's client ID. |
| Client Secret | The integration's client secret. |
| Domain Restrictions | Optional. A comma-separated list of email domains that may sign in. |
| Allow auto link to existing account | Links a first Okta sign-in to an existing user with the same email. |
| Reject unknown identities | Reject refuses Okta users who have no user in your app; Allow sign-up lets them register through the Signup component. |
Tadabase asks Okta for the openid, profile and email scopes. Save your changes.
4. Add the Okta buttons #
Add Login With Okta (SSO) to your Login component and Signup With Okta (SSO) to your Signup component, then test in a private browser window. When someone signs up through Okta, Tadabase fills the new user's name and email from Okta. See Set up a provider.
To stop password sign-in once Okta works, turn on Single sign-on only: see Options on every provider card.
Was this page helpful?
Something wrong or missing on this page? Tell us.